A risk register is valuable only when it changes a decision or an action. A risk register presentation should therefore show exposure, owner, mitigation status and the choices leadership must make. It should not turn every uncertain detail into a red bubble or imply that a low score means a risk is gone.
If you are combining status evidence into a concise deck, the data storytelling for presentations guide offers a useful structure for connecting evidence to a decision. This article applies that structure to risk reporting.
1. Set the purpose and risk boundary
State the review question first: “Which delivery risks need an executive decision this month?” Define the project, reporting date and risk appetite that apply. A construction rollout, a software migration and a customer launch may use different thresholds; there is no universal red, amber and green rule.
Explain what counts as a risk in this review. A risk is an uncertain event or condition that could affect an objective. An issue has already happened and needs active resolution. A dependency is something the work relies on. Keeping those categories separate prevents a past incident from being presented as a future probability.
Show the objectives that matter: timeline, service level, cost, security, quality or customer experience. Without an objective, the audience cannot judge impact.
2. Select fields that support action
A practical register can include risk statement, cause, event, impact, likelihood, impact rating, exposure, owner, mitigation, due date, status and residual risk. Use a short sentence such as “If the identity migration slips, the launch date may move because the new workflow cannot be tested end to end.”
Keep cause, event and impact distinct. “Vendor is late” is an event; “contract approval is still pending” may be a cause; “pilot testing loses two weeks” is an impact. This structure makes the mitigation more precise.
Limit the presentation to risks that require attention. A full register can remain in the working tool or appendix. The main deck should highlight new, worsening, overdue or decision-blocking items, plus any risk the audience needs to accept.
3. Make the scoring method visible
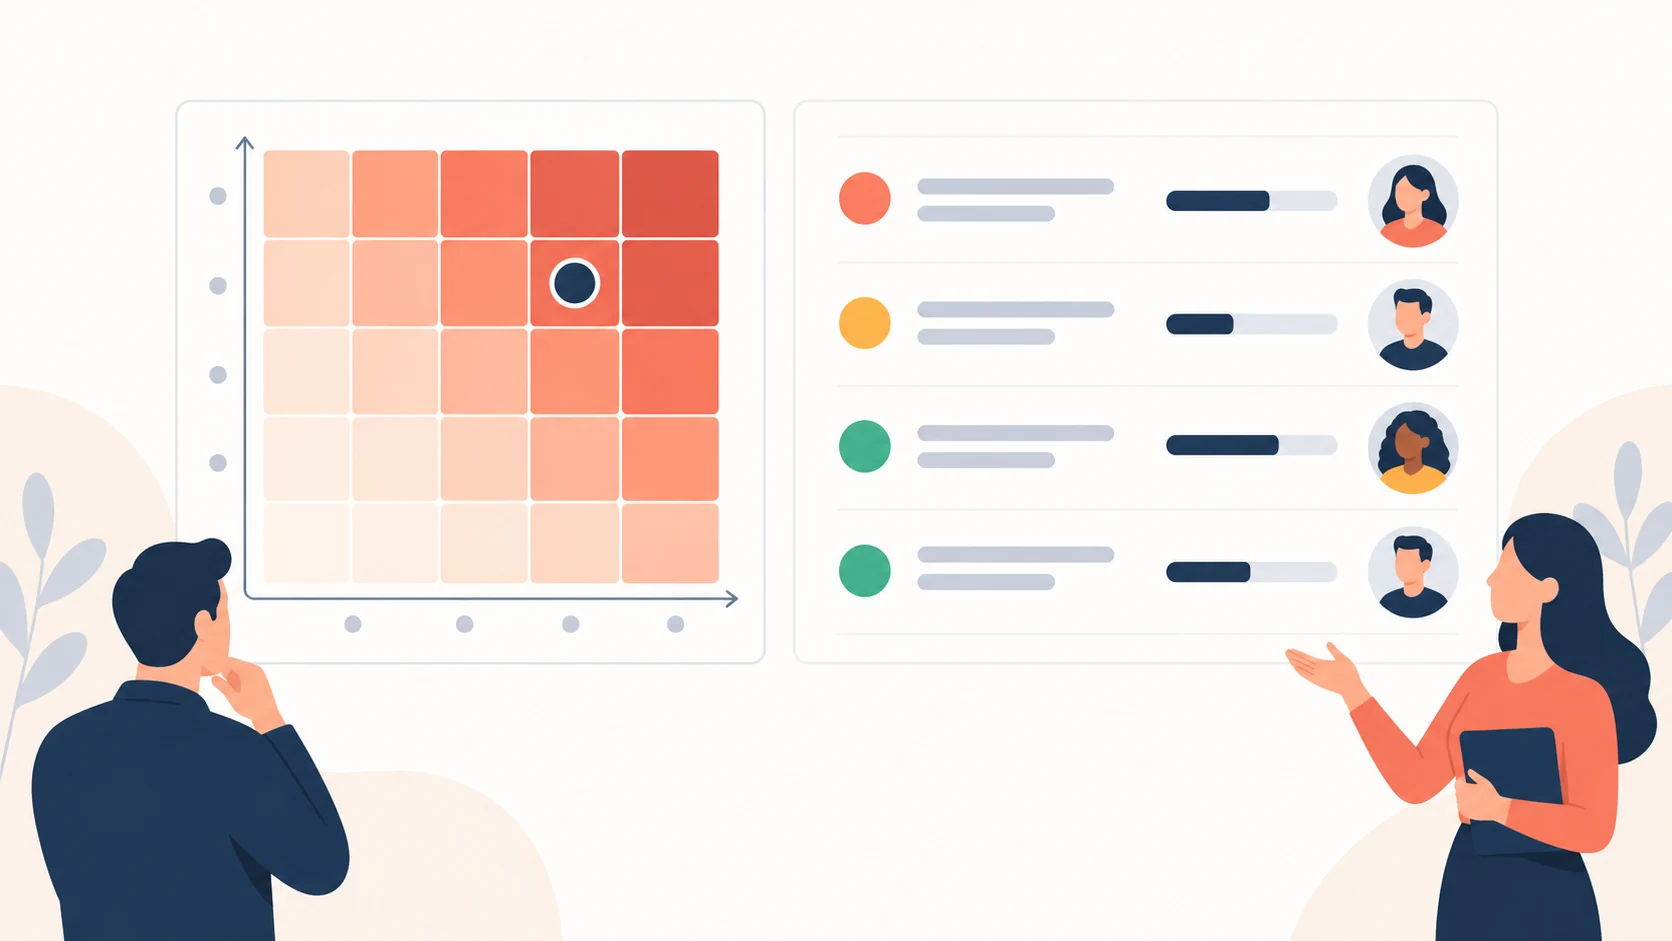
Describe the scale in plain language. For example, likelihood might be rare, possible or likely, while impact could be minor, material or severe. Define the period and objective used for each rating. A score without a time horizon is difficult to interpret.
If you multiply likelihood and impact, show that it is a prioritization aid, not a probability of loss. A risk scored 3 × 4 is not automatically twice as serious as one scored 2 × 4. Use the total to decide where to look first, then explain the actual consequence and evidence.
Show confidence separately when the evidence is weak. A high-impact, low-confidence risk may deserve discovery; a high-impact, high-confidence risk may require immediate mitigation. This is more useful than hiding uncertainty inside one color.
4. Report mitigation as work with a result
Write mitigation as an action that has an owner and completion signal. “Monitor the vendor” is vague. “Run a weekly interface test, owned by the integration lead, until three consecutive builds pass” has a visible result. The right signal depends on the risk; do not invent a metric simply to fill a column.
Distinguish preventive controls from contingency plans. A preventive control reduces likelihood or impact before the event. A contingency describes what the team will do if the event occurs. Include both when they lead to different owners or decisions.
Report status honestly: not started, in progress, blocked, completed or accepted. A completed mitigation does not mean residual risk is zero. Show the remaining exposure and the next review date.
5. Make ownership and escalation explicit
Assign one accountable owner for each top risk. Contributors can support the work, but the audience should know who will report a change and who can authorize the response. Do not assign a risk to an entire department.
Set an escalation rule before the risk becomes urgent. For example, escalate when a mitigation is blocked for two reporting cycles, a threshold is exceeded or a decision is needed outside the project team. The rule should fit the project’s governance; the example is only a prompt for discussion.
Use the final slide to list decisions requested, acceptance of residual risk and the next checkpoint. If no decision is needed, say what the team will continue to monitor and when the register will be reviewed again.
6. Build a readable risk presentation
A compact deck can use this sequence: objective and risk boundary; top risks by exposure; one slide per decision-blocking risk; mitigation and residual risk; decisions and owners. Keep the full register available for detail, but do not force every row into the meeting narrative.
Use stable labels and dates. A red item from last month should not be assumed to mean the same thing today. Add a “changed since last review” marker when it helps the audience focus. Use color as a support for labels, never as the only signal.
Ask a reviewer to name the top risk and the next owner after reading the deck. If they cannot, reduce the number of items or move context closer to the decision. A good risk register presentation helps people act while preserving the limits of what the register can prove.